With Guardey, healthcare consulting firms and healthcare institutions quickly and easily train their staff against cybercrime.
No payment information needed.





About 30 percent of all hacks occur annually at a healthcare facility. In the first half of 2021, 66 healthcare sites were affected in Europe.

Malicious hackers target healthcare facilities because they are more likely to pay. They work with sensitive information and cannot be shut down for days. In fact, without IT systems, the entire hospital is at a standstill. That has major consequences.
Pharmacists are also at risk because drug production cannot come to a halt.
In-house staff is not always aware of the risks. Healthcare professionals are, fortunately, busy with very different things. But One click on the wrong link in a phishing email and patient data is out on the street.
Time to secure your patients even better. That’s where Guardey is going to help.
Healthcare organizations are very interesting to hackers. Why?

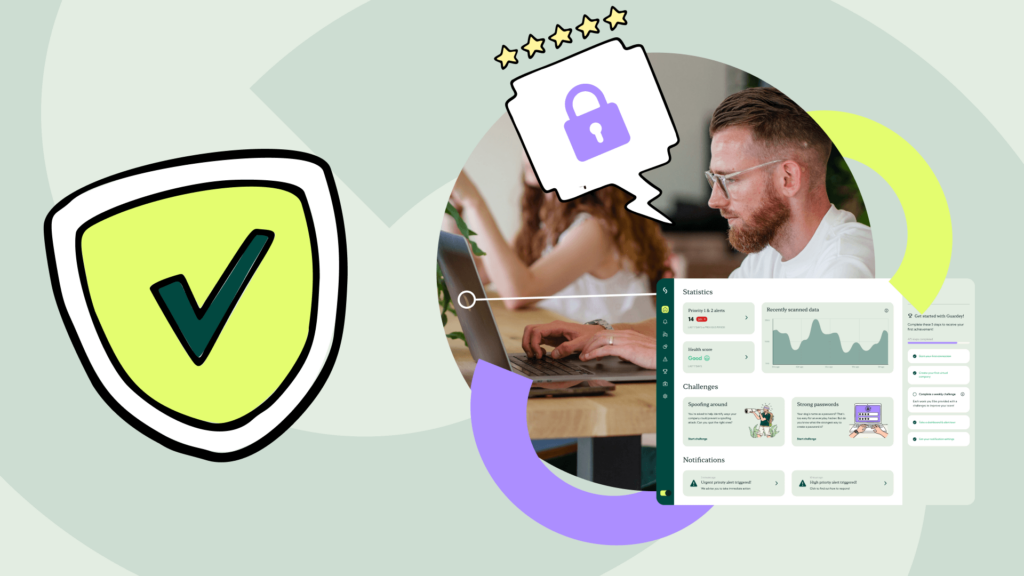
One click on the wrong link and patient data is out on the street. Guardey trains healthcare staff in a few minutes a week, so security fits into a busy schedule.
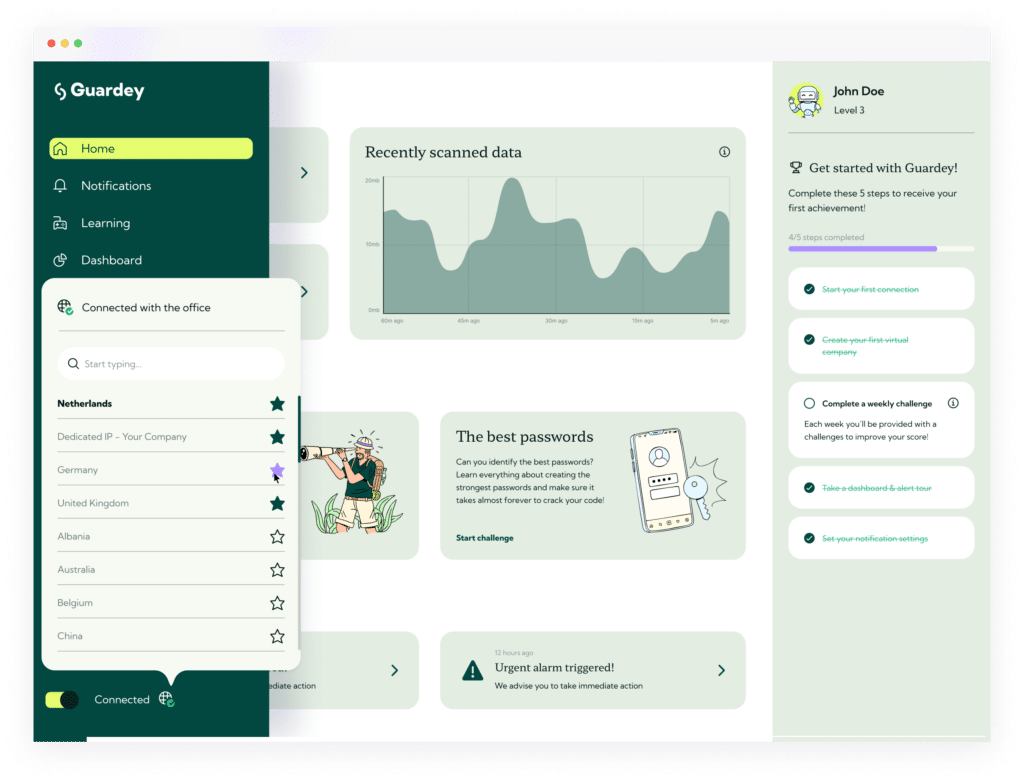

“As a medical institution, we have specific security measurements in place to protect patient data. This includes how we control access to our computers, the place of personal electronic devices at work, and how to act in case of a cybersecurity-related issue. So we wanted to be able to customize the training content to add that information.”
Kim van Polanen
Operational ManagerGamification is adding game elements into non-game environments, such as security awareness training, to increase participation and foster active learning.
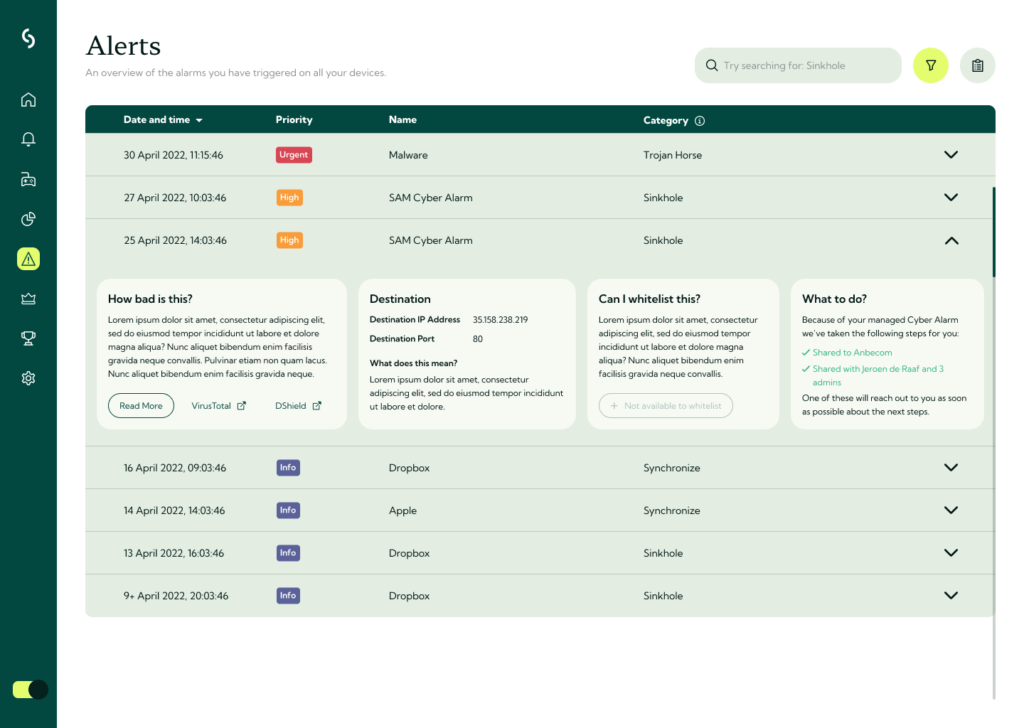
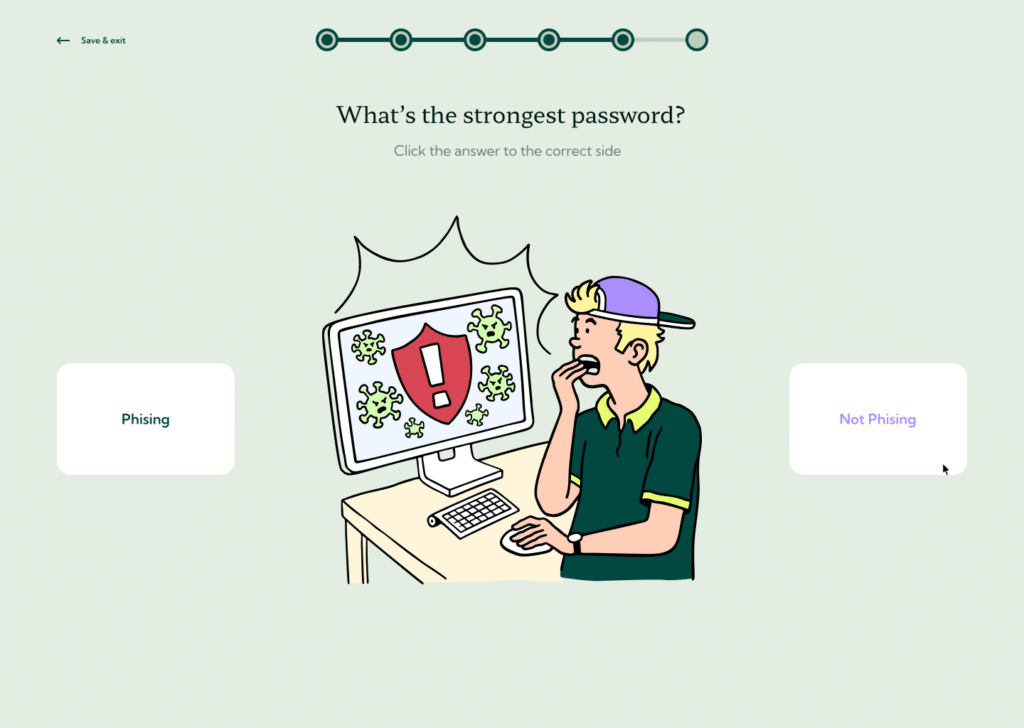
Traditional security awareness training can often be dry and boring. With gamification, the complex subject matter is transformed into an engaging and memorable experience.
By integrating game elements such as challenges, quizzes and rewards, it incentivizes users to actively learn. This makes the training more enjoyable and fosters a sense of competition and achievement. This combination drives better retention and application of cyber security knowledge.
Research shows that up to 90% of the learnings from yearly or even quarterly training are forgotten within a few weeks. Guardey was built to keep its users aware of cyber threats 365 days a year. The game comes with short, weekly challenges that slowly builds up the user’s knowledge and eventually drives lasting behavior change.
Guardey covers a wide array of topics to train users about all currently relevant cyber threats, put together in collaboration with ethical hackers and educationalists. The topics covered include phishing, remote work, password security, CEO fraud, ransomware, smishing, and much more.
Every challenge takes up to three minutes to complete.
Yes. ISO27001, NIS2, and GDPR all require that all employees receive appropriate security awareness training. Guardey is always up-to-date with the latest cyber threats, policies, and procedures.
Cybersecurity awareness training is crucial for all employees, not just specific roles. Every staff member can potentially be a target or an unwitting entry point for cyber attacks. Training helps create a security-focused culture and minimizes risks for the entire organization.
While certain roles may require specialized training, a foundational level of training should be accessible to everyone.
Guardey is available in English, Dutch, Italian, French, Spanish, German, Polish, Swedish and Danish.

