

Security awareness training
Three-minute gamified challenges, phishing simulations and audit-ready reporting. Covers the Article 21 training obligation for every employee.
NIS2 covers more organisations than most expect: 18 sectors, from 50 staff or €10 million in turnover, some regardless of size. And if you supply an organisation that is in scope, its obligations reach you through the contract.
Three-minute gamified challenges, phishing simulations and audit-ready reporting. Covers the Article 21 training obligation for every employee.
Short modules on what Article 20 requires of the management body, with a certificate you can use as evidence of director training.
Guardey is built and hosted entirely within the EU, so your training data stays under European jurisdiction. No transfers outside the EU, giving you clarity around data residency and GDPR.

Three-minute challenges keep employees coming back instead of dreading another mandatory course. Streaks, levels, and rewards turn security awareness into a lasting habit.
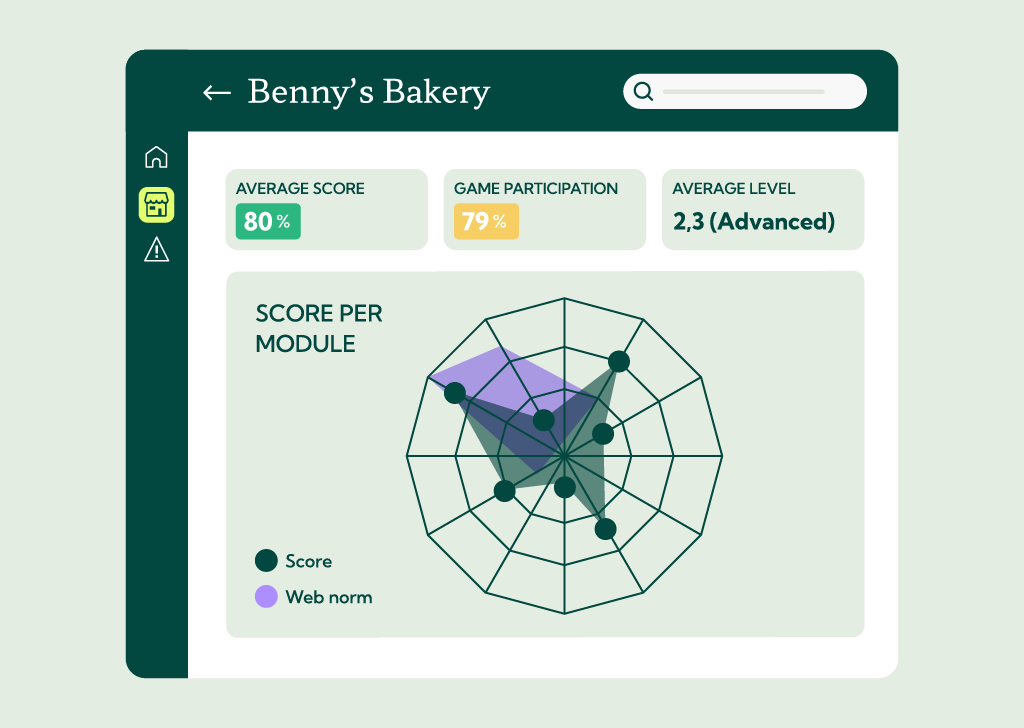
Track completion, scores, and progress across your organization with audit-ready reporting that helps demonstrate your NIS2 awareness efforts.
Answer 4 questions about your organisation. You get a readiness score, the obligations you already meet, and the gaps to close first.
Get your free 15-page guide covering everything you need to know about NIS2. Learn who needs to comply, understand the key requirements, follow a practical compliance checklist, and discover how to prepare your organization for NIS2.
NIS2 covers essential and important entities across 18 sectors, including energy, transport, healthcare, banking, digital infrastructure and manufacturing. Size thresholds apply: generally 50+ staff or €10 million or more in turnover, though some sectors are covered regardless of size. The test tells you which category you fall into.
Both must meet the same security obligations. The difference is supervision: essential entities face proactive supervision and audits, important entities are supervised reactively after an incident. Fines differ too, up to €10 million or 2% of turnover for essential, up to €7 million or 1.4% for important.
Yes. Article 21 lists basic cyber hygiene practices and cybersecurity training among the minimum measures organisations must take. You need to be able to evidence it, which is where reporting matters.
Article 20 requires management bodies to approve the cybersecurity risk-management measures, oversee their implementation, and follow training themselves. Member states can hold leadership personally accountable for failures.
An early warning within 24 hours of becoming aware of a significant incident, an incident notification within 72 hours, and a final report within one month.