

10 September 2026 • Cyber security
Most cyber attacks do not start with a forced lock. They start on an ordinary working day: someone clicks a link in what looks like an invoice, reuses a private password at work, or sends a file over the airport Wi-Fi. Around 60% of all hacks and data breaches involve a human element like that, according to Verizon’s Data Breach Investigations Report.
That sounds like bad news, and it is quietly the best news in cyber security. You will never patch every piece of software in time, but you can change what people do. Organizations with a strong security culture have fewer incidents, and they notice the ones they do have sooner, because employees recognize when something is off and say so.
This guide covers what security awareness is, why it has become a legal requirement for thousands of European organizations, where the stakes are highest, and how to build a program that changes behavior instead of ticking a box.
In short
- What it is: security awareness is the everyday ability of your people to recognize a cyber risk and act on it, from a strange invoice to a request that feels too urgent.
- Why it matters: around 60% of breaches involve a human element, and ransomware plays a part in 88% of breaches at small and medium-sized businesses.
- It is now law: NIS2 requires management to be trained and expects training for every employee, and member states have now written that requirement into national law.
- Highest stakes: healthcare and education hold sensitive personal data, so one careless click affects patients, students and families, not just the organization.
- What works: support from leadership, clear policies, short recurring training and realistic phishing simulations, communicated in a positive tone.
- What does not: a single annual session. Knowledge fades within weeks and behavior never changes.
What is security awareness: a definition
Security awareness refers to an understanding of cyber threats and best practices for safeguarding sensitive information and systems. It involves recognizing potential risks, adhering to secure behaviors, and staying informed about evolving cyber threats to protect against data breaches, malware, and other online security challenges.
Why security awareness is more important than ever
There are a lot of misconceptions about security awareness. Here are a few we hear a lot:
→ “Security is the responsibility of the IT department, not mine”
→ “Cyber criminals are too advanced for security awareness training to be effective”
→ “Cyber criminals only hack huge corporations, why would they target me?”
→ “My employees don’t need training, they’re experienced internet users”
As stated in the intro of this article, around 60% of all breaches involve a human element, according to Verizon’s 2025 Data Breach Investigations Report. No matter how much cyber security software you have in place, it can’t protect you from human mistakes such as clicking a phishing link or using weak passwords. This means that every single employee within your organization carries the responsibility to keep your company data safe.
Many of the tactics that cyber criminals use are not as advanced as people think. Once your team is aware of the basics, the chances of a data breach decrease by a lot. For instance, most data leaks are still caused by weak passwords and the absence of two-factor authentication.
Here is an example of an ethical hacker hacking an organization’s system. Not with fancy tooling, but with simple social engineering:
If your organization is aware of these threats and has the right procedures in place, examples of hacks like this are way less likely to occur.
Most big corporations have invested thoroughly in cyber security. That’s why cyber criminals are widening their scope and targeting companies of any size. Verizon’s 2025 report shows that ransomware is involved in 88% of breaches at small and medium-sized businesses, compared to 39% at large organizations. And the pressure keeps rising: Check Point counted an average of 1,968 attacks per organization per week in 2025, 70% more than in 2023.
On top of that, security awareness is increasingly a legal obligation. The European NIS2 directive requires management to follow cyber security training and expects organizations to offer similar training to all employees. Member states have translated the directive into national law, so the obligation now lands with far more organizations than the old rules did. Read more about the requirements in our NIS2 overview.
All the above means that it’s a must for companies of all sizes to invest in security awareness for their entire organization.
Where security awareness matters most: healthcare and education
Every organization has something worth stealing, but not every leak does the same damage. In healthcare, a single mailbox can hold medical files, care plans and correspondence about someone’s treatment. In education, schools keep student records, home situations, care reports and photos of minors. That kind of data cannot be reissued the way a bank card can. Once it is out, it stays out.
The working day in those sectors adds to the risk. Staff move between systems and shared devices, they work under time pressure with a patient or a classroom in front of them, and IT support is often one person for the whole organization. Attackers know this, which is why fake invoices to school administrations and supplier emails to care institutions keep working.
It is also why phishing simulations earn their place here. They show, without blame, what really happens when a convincing message lands on a busy Tuesday morning. That is a lot more honest than a survey asking people how alert they think they are.
The urgency is not limited to care and education. NIS2 sets the same baseline for energy, water, transport, manufacturing, digital services, waste and food, and it holds management accountable for it. Sectors handling the most sensitive data simply feel it first. The direction for everyone else is the same: treating other people’s data with care is turning into a basic requirement rather than something you stand out with.
How to develop security awareness within an organization
To develop a strong security awareness program within your organization, you’ll need to take the following steps.
Get buy-in from leadership
Before you start any security awareness campaigns, make sure to get support from your leadership team. If leadership is not invested, all your hard work will be for nothing in the end. If your CEO doesn’t care, why should the rest of the company feel invested?
Share the importance of security awareness (or simply share this article 😉 ) and create a regular cadence in which you update them on ongoing security projects.
Once your leadership team truly believes in the necessity of cyber security awareness, you can start focusing on the so-called departmental champions. These are often team leads who are closer to the rest of the company and may need to help you carry out security initiatives. They are the people through which you communicate concerns and new security measures.
If you work in a larger organization and you need to convince a lot of stakeholders, it can be helpful to keep track of them in a stakeholder management template.
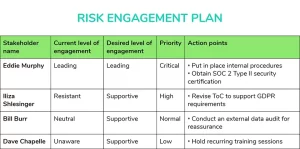
When presenting your plans to the leadership team, it’s important to make clear that this is a long term program. If this is not clear, some people may think you’ll organize a one-off event. But your awareness program needs to be a marathon, not a sprint, to be effective.
Set up clear policies and procedures
Security policies and procedures are the bedrock of any organization’s defense against cyber attacks. These policies serve as a set of guidelines that not only define how to protect data, systems, and networks but also dictate how employees should behave in the digital world.
Two examples of essential security policies are:
- Data access control policy: This policy outlines who can access sensitive data and under what circumstances. It defines user roles and permissions, access authentication methods, and restrictions on data sharing. This prevents unauthorized people from viewing and modifying confidential information.
- Password policy: A robust password policy establishes guidelines for creating and managing passwords. It dictates criteria for password complexity, expiration, and protection. This reduces the risk of unauthorized account access.
You also need clear procedures for how employees should act when faced with a cyber threat or even a breach.
Set up recurring employee training
Once you’ve got buy-in from the leadership team, it’s time to set up security awareness training for everybody within the organization. During these trainings, employees should learn about all relevant cyber threats, which we’ll go through later in this article.
Not sure where your team stands today? Start with a security awareness baseline measurement and you have a clear starting point to measure progress against.
When looking for a training solution, consider the following aspects:
- Pick a training solution that is based on gamification. A security awareness game like Guardey enables users to learn actively.
- Offer training that is recurring. Companies often offer yearly training that gives a quick knowledge boost but doesn’t result in lasting behavior change. Look for training solutions that offer weekly, bite-sized training.
- Make sure that you offer training on all current cyber threats. For instance, if a training solution has no content about the threats of AI, it’s not the right solution. Cyber criminals are moving fast, which means your training solution should develop just as fast to keep your employees in the know.
Not sure what security awareness training actually looks like?
See how a weekly 3-minute challenge, built together with ethical hackers, turns awareness into a habit your team keeps.
Discover security awareness trainingFrame your program with a positive tone
There is often a negative tone attached to communication surrounding cyber security. When employees fail a phishing test or don’t get high scores during awareness training, they may feel like they’ll get judged or even punished for it. That’s why it’s key to position your program as something that benefits both your organization and the employee.
With that in mind, also understand that people will not care about your security program the same way that you do. Communicating the why can therefore truly make a big difference. Paint a vivid picture of what the impact can be when there is no security awareness program.
Measure what changes, not what people know
A quiz score tells you what someone remembered for five minutes. What you want to know is what they do. Track how many people click a simulated phishing mail, how many report it and how fast, then watch those two numbers over the months. A team whose report rate climbs is a team that has started to look, and that is the number worth putting in front of your leadership team.
Behavior moves slowly, so give it seasons rather than weeks. If you took a baseline measurement at the start, you have something honest to compare against.
Which cyber threats should be included in training?
Security awareness entails more than just phishing and password management. When training your personnel, you need to make sure that you cover every cyber threat that you may face. Here is a far-from-complete list that gives you an idea of threats you that should be included in training.
- Phishing attacks: Teach your team to recognize phishing emails and suspicious links, and emphasize the importance of not sharing sensitive information with unknown sources. Test whether the message sticks with recurring phishing simulations.
- Ransomware: Provide guidance on identifying potential ransomware threats and stress the importance of regularly backing up data.
- Social engineering: Train employees to be cautious about sharing sensitive information in person, over the phone, or online, and to verify the identity of people requesting confidential data.
- Password security: Promote strong password practices, including using complex and unique passwords, enabling two-factor authentication, and avoiding password sharing.
- Malware: Educate employees about the risks of downloading software or files from untrusted sources and the importance of using reputable antivirus software.
- Insider threats: Create awareness about the potential for malicious actions by employees or partners, emphasizing the need for a culture of both vigilance and trust.
- BYOD (Bring Your Own Device) risks: Provide guidelines for securely using personal devices in the workplace and recognizing the potential security threats associated with them.
- Data handling and protection: Instruct employees on how to properly handle, store, and transmit sensitive data to prevent data breaches and unauthorized access.
- Wi-Fi security: Educate employees on the dangers of using unsecured public Wi-Fi networks and the importance of using a virtual private network (VPN) when necessary.
- Email security: Highlight email best practices, such as verifying email senders, not opening attachments or clicking on links in suspicious emails, and reporting phishing attempts.
And the list goes on and on. If a security awareness training solution doesn’t cover a few of the above topics, consider it incomplete and not the right fit.
The bottom line
Contrary to popular belief, you can in fact outsmart hackers. Security aware organizations are simply less likely to be hurt by cyber attacks. The most hacks and data leaks still happen due to simple human errors: clicking phishing links, working from an unsecured network, or not using two-factor authentication.
To establish cyber security awareness within your organization, you should consider offering regular security awareness training. This enables your employees to learn about the biggest cyber risks and act accordingly when faced with one.
With Guardey’s security awareness game, your team gets a weekly 3-minute challenge about a specific security topic. The game is put together in collaboration with ethical hackers and educationalists to accomplish lasting behavior change. You can now start a 14-day free trial.
Frequently asked questions about security awareness
What is security awareness?
Security awareness is the understanding of cyber threats and safe behavior among everyone in your organization, digital and physical alike. It means recognizing phishing, handling sensitive data with care and knowing what to do when something goes wrong. It is a skill you maintain, not a one-off exercise.
Why is security awareness important?
Around 60% of all breaches involve a human element, which makes your employees the deciding factor between an attempted attack and an actual incident. On top of that, legislation such as NIS2 requires organizations to train both management and employees.
How often should employees get security awareness training?
Short and frequent beats long and rare. A yearly session is forgotten within weeks, while short weekly trainings keep knowledge fresh and gradually change behavior. That rhythm is exactly what turns awareness into a habit.
What is the difference between security awareness and security awareness training?
Security awareness is the goal: employees who recognize cyber risks and act on them. Security awareness training is the way to get there, with a structured program that builds knowledge and safe behavior step by step.
Is security awareness different in healthcare and education?
The threats are the same, the consequences are not. Care organizations and schools work with medical files, student records and home situations, so a leak hits people who never chose to take that risk. The practical difference sits in the training itself: short sessions that fit between patients or lessons, examples from their own working day, and a culture where reporting a mistake is normal instead of punished. Dutch primary and secondary schools, for example, are working toward the normenkader IBP, in which staff awareness is one of the norms.
Ready to put the guide into practice?
Run it with your own team and see within two weeks who recognizes a phishing mail and who clicks. Free to try, and you can stop whenever you want.
Try Guardey free for 14 days


