8 April 2023 • NIS2
In brief: NIS2 (Directive (EU) 2022/2555) replaced NIS1 (Directive (EU) 2016/1148) on 18 October 2024. The biggest differences: NIS2 covers 18 sectors instead of 7, applies automatically to medium and large companies in those sectors, sets fixed incident-reporting deadlines (24 hours, 72 hours, one month), introduces EU-wide maximum fines (up to €10 million or 2% of global turnover) and makes management personally liable. If you were under NIS1, you are under NIS2 now, with stricter rules.
Below you find what NIS1 was, every difference side by side, what changes if you were already under NIS1, and where each EU country stands with implementation in 2026.
What was NIS1?
NIS1, officially Directive (EU) 2016/1148, was the EU’s first cybersecurity law. It was adopted on 6 July 2016 and had to be transposed into national law by 9 May 2018. It applied to two groups:
- Operators of essential services (OES) in seven sectors: energy, transport, banking, financial market infrastructures, health, drinking water and digital infrastructure. Each member state decided itself which companies counted as “essential”, which led to large differences between countries.
- Digital service providers (DSP): online marketplaces, online search engines and cloud computing services.
NIS1 required “appropriate and proportionate” security measures and reporting of incidents “without undue delay”, but set no deadlines, no minimum list of measures and no harmonised fines. In practice, many organizations in the same sector faced completely different obligations depending on the country. That inconsistency is the main reason NIS2 exists.
NIS1 was repealed on 18 October 2024. If you still see “NIS” or “NIS1” in a contract, tender or policy, it should now be read as NIS2. The national NIS1 laws it produced are still useful as background: see our pages on the Dutch Wbni and the UK NIS Regulations 2018 (the UK kept its own NIS regime after Brexit and is not covered by NIS2).
What is the NIS2 guideline?
NIS2 is the successor to NIS1, which was introduced years back for essential businesses. The new NIS2 directive (officially: Directive (EU) 2022/2555)) was adopted by the European Parliament and the Council on 14 December 2022 and published in the Official Journal of the EU. ENISA, the EU Agency for Cybersecurity, supports member states with its implementation. The directive prescribes minimum security requirements, as well as the obligation to report (serious) incidents to the national authority or the European Computer Security Incident Response Team (CSIRT). The new directive replaces the original one, which came into force in 2016.
Does NIS2 replace NIS1?
Yes. NIS2 fully replaces NIS1. When NIS2 became applicable in October 2024, the original NIS directive from 2016 was repealed. Everything that fell under NIS1 now falls under NIS2, together with many new sectors and stricter requirements.
These are the main differences between the NIS1 and NIS2:
- Directive applies to more sectors
The NIS2 applies to essential companies as well as major companies. More medium-sized and large companies must start complying with the directive. In addition, each member state may designate smaller companies with a high security risk that must also comply. - List of minimum basic security
The directive is more concrete, thanks to a list of minimum basic security that companies must implement. The directive imposes a risk management approach. - Division into essential and key sectors
The new NIS directive divides companies into essential and key sectors. The distinction between operators of essential services and providers of digital services disappears. - Address security in the chain
Companies must start addressing security risks in their supply chain. That includes risks created by supplier relationships. - Stricter supervision
National authorities are allowed stricter supervision and enforcement. The new directive pulls penalty regimes and reporting requirements in all member states equal(er).
NIS1 vs NIS2: all differences side by side
| NIS1 | NIS2 | |
|---|---|---|
| Legal basis | Directive (EU) 2016/1148 | Directive (EU) 2022/2555 |
| Adopted / applies from | 6 July 2016 / 9 May 2018 | 14 December 2022 / 18 October 2024 |
| Sectors | 7 sectors plus digital service providers | 18 sectors: 11 “high criticality” (energy, transport, banking, financial market infrastructure, health, drinking water, waste water, digital infrastructure, ICT service management, public administration, space) and 7 “other critical” (postal, waste, chemicals, food, manufacturing, digital providers, research) |
| Who is in scope | Companies designated by each member state | Automatically: all medium and large companies in those sectors (50+ employees or €10 million turnover), plus smaller ones designated as critical |
| Entity categories | Operators of essential services, digital service providers | Essential entities, important entities |
| Security measures | “Appropriate and proportionate”, not specified | Minimum list of 10 measures (Article 21), including risk analysis, incident handling, business continuity, supply chain security, MFA and cyber hygiene and security awareness training |
| Incident reporting | “Without undue delay”, no fixed deadline | Early warning within 24 hours, notification within 72 hours, final report within one month |
| Supply chain | Not addressed | Explicit obligation to manage supplier and service-provider risk |
| Management liability | None | Management must approve and oversee measures, follow training, and can be held personally liable |
| Maximum fines | Set per member state, “effective, proportionate and dissuasive” | Essential: €10 million or 2% of global turnover. Important: €7 million or 1.4%. Whichever is higher. |
| Supervision | Light, varied per country | Essential entities: proactive (ex-ante) supervision incl. audits. Important entities: reactive (ex-post) supervision after indications of non-compliance |
| Registration | No | Entities must register with the national authority |
What are essential businesses?
The NIS directive applies to essential businesses. These sectors are:
- Energy
- Drinking water
- Wastewater
- Transportation
- Banking
- Financial Markets
- Digital infrastructure
- Public Administrations
- Health care
- Space
Tip: Wondering exactly which companies are “essential” or “important”? Download the table Sectors covered by NIB2 from CBS.
The new NIS2 directive will also apply to major companies. These sectors are:
- Postal and courier services
- Processing and distribution
- Waste processing
- Digital providers
- Manufacturing companies
- Chemical industry
- Food industry
Difference in supervision between essential and important companies
Local authorities will proactively monitor key businesses. Supervision of key businesses will take place after the fact, if there is evidence of an incident.
Key and essential companies will have a duty to report and a duty of care. They have to put security in place in their supply chain and communicate clearly how they handle cyber incidents.
Why is the new guideline important?
The new NIS2 directive should make network and information systems at companies more secure. In this way, the Netherlands and the entire European Union should become less vulnerable to cyber attacks.
Minister Dilan Yeşilgöz-Zegerius (Justice and Security) said, “We are increasingly dependent on digital processes, especially since corona we are working more and more from home. In addition, we see a growing digital threat from both criminals and state actors that, with a war on Europe’s eastern border, is not going to abate for the time being. It is therefore now necessary to take the next step to raise the level of cybersecurity in the EU. In doing so, we will prevent digital incidents from disrupting our society.”
Minister Micky Adriaansens (Economic Affairs and Climate) adds: “We must be alert to the risks of cyber attacks. The impact can be significant, such as empty shelves in stores or industrial production outages. Managing digital security remains an individual responsibility of companies and consumers. But with this legislation we can take a step to ensure that the level of cyber security goes up among (medium) sized parties in more important sectors.”
Is your organization ready for NIS2?
NIS2 requires cyber security training for your employees and your board. Guardey makes it easy with gamified security awareness training that takes just a few minutes per week.
Start your free 14-day trial
Will you be fined if you fail to comply?
Companies that fail to comply with the new directive will receive a warning, then a reminder and then risk a large fine. For essential companies, the maximum fine is 10 million euros or 2 percent of the worldwide annual turnover, whichever is higher. For important companies, the maximum is 7 million euros or 1.4 percent. New in NIS2: management can also be held personally liable for non-compliance.
Accountability also reaches the top of the organisation: under Article 20, management bodies answer for these measures and must follow training themselves. See how NIS2 training for executives works.
You were under NIS1: what changes for you
If your organization was an operator of essential services under NIS1, you are almost certainly an essential entity under NIS2. In practice, six things change:
- Your obligations are now specified. The ten minimum measures in Article 21 replace the open norm. Map your current controls against that list; most NIS1 organizations find gaps in supply chain security and in training.
- Reporting has a clock. 24 hours for an early warning, 72 hours for the notification, one month for the final report. Check that your incident process can produce a first notification within a day, including at the weekend.
- The board is in the loop by law. Management approves the measures, follows training itself and is liable. Put NIS2 on the board agenda with a named owner.
- Training is no longer optional. Article 21(2)(g) requires basic cyber hygiene practices and cybersecurity training for staff. A yearly slide deck will not satisfy an auditor asking for evidence; continuous training with completion data will.
- Your suppliers are your problem. You must assess the security of suppliers and service providers. Expect to receive the same questionnaires from your own customers.
- Expect to be audited. Essential entities fall under proactive supervision. Keep evidence (policies, training records, incident logs) in one place.
NIS2 implementation per EU country (2026)
NIS2 is a European directive, so every member state has to turn it into national law. Not every country moves at the same speed. This is where the main markets stand in 2026:
- Belgium: one of the first to transpose. The Belgian NIS2 law has applied since October 18, 2024, supervised by the Centre for Cybersecurity Belgium (CCB).
- Italy: transposed early through Legislative Decree 138/2024, in force since October 2024. The national cybersecurity agency ACN supervises registration and compliance.
- Germany: the NIS2UmsuCG entered into force on December 6, 2025. Around 29,500 companies fall under the law and had to register with the BSI.
- Poland: the amended National Cybersecurity System Act (KSC) entered into force on April 3, 2026 and covers roughly 42,000 companies, with a registration deadline in October 2026.
- The Netherlands: the Cyberbeveiligingswet was adopted in July 2026 and enters into force on August 15, 2026, without a transition period.
- France: still in the legislative process. The Loi Résilience is expected to pass in 2026, but ANSSI already encourages organizations to register and prepare.
- Spain: the draft law on cybersecurity coordination and governance is still going through parliament, so the directive is not yet fully transposed.
The takeaway: no matter where you are in the EU, the training and risk management obligations of NIS2 either already apply to you or will very soon.
NIS2 vs ISO 27001: what is the difference?
NIS2 is legislation, while ISO 27001 is a voluntary international standard for information security. An ISO 27001 certificate is not legally required and does not automatically make you NIS2 compliant. There is plenty of overlap though: organizations that follow ISO 27001 already cover a large part of what NIS2 asks for, such as risk management, incident procedures and security awareness training.
Preventing damage from cybercrime: what can you do?
Even without a cyber law like NIS2, it is important to take cybercrime seriously. You protect your business with, for example:
- Security by design
Start every meeting with (digital) security. What measures do you take to prevent abuse and what are the risks and vulnerabilities? By thinking about this as standard, you set up (new) systems more secure by default. - Secure connection
Make sure employees connect securely, also when they work from home or on the road. Protect access to company systems with multi-factor authentication and avoid open public wifi for company data. - Train employees in cybersecurity
Those who do not know what the risks are cannot possibly protect themselves against them. Train employees and make sure they recognize vulnerabilities and don’t fall into traps when cybercriminals set them up.
Frequently asked questions about NIS1 and NIS2
Is NIS1 still valid?
No. NIS1 was repealed on 18 October 2024, the day NIS2 became applicable. References to “NIS” in older documents should be read as NIS2.
Does NIS2 replace NIS1 completely?
Yes. There is no transition period in which both apply. Member states that transposed NIS2 late (such as the Netherlands and Germany) enforced NIS1 national law until their NIS2 law entered into force.
What is the main difference between NIS1 and NIS2?
Scope and enforceability. NIS2 covers roughly ten times more organizations, specifies the measures, sets reporting deadlines and introduces EU-wide fines and management liability.
Was I under NIS1 if I am under NIS2?
Not necessarily. Most organizations under NIS2 are new to this type of regulation: medium-sized manufacturers, food companies, waste processors, postal services and research organizations were not covered by NIS1 at all.
Does NIS2 require security awareness training?
Yes. Article 21(2)(g) lists “basic cyber hygiene practices and cybersecurity training” as a minimum measure, and Article 20 requires management to follow training as well.
How EyeOn uses Guardey to comply with NIS2
Companies that need to comply with NIS2 are required to offer security awareness training to their employees. This obligation explicitly includes the board: under article 20 of the directive, management must follow cyber security training too.
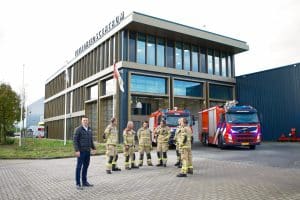
Our customer Gezamenlijke Brandweer Amsterdam (a Dutch fire department) is an essential organization and therefore needs to adhere to the NIS2 regulation. To ensure their employees are prepared to recognize cyber threats, they use Guardey to offer security awareness training. Every week, their team plays a short challenge of about three minutes that helps them to slowly build up cyber security knowledge.
Make it easy with Guardey
We understand at Guardey that you may have a lot on your mind. How do you comply with NIS2, what are the vulnerabilities at your company and how do you prevent a hack, data breach or other cybercrime?
That’s why we make the human side of NIS2 easy. NIS2 requires organisations to train their people in cyber hygiene, and board members too. With Guardey, employees build that awareness step by step in short, gamified challenges of three minutes a week. Realistic phishing simulations show who recognises an attack, and the reports give you the proof your auditor asks for.
So do you want to get your team ready for NIS2? Discover our security awareness training or ask us your questions. We’ll be happy to explain how Guardey fits your organisation.
Want to dive deeper into NIS2?
Our NIS2 guide explains the requirements step by step: who falls under the directive, what you need to arrange and how to get your team ready.
Read the NIS2 guide